Virtru Developer Experience
Virtru Data Harbor Platform SDKs and APIs
Build Access Control Into The Data - Wrap data in the Trusted Data Format (TDF) and enforce attribute-based access control (ABAC) on every request, under your policy. Read the docs, run the quickstart, and build a prototype without talking to anyone.
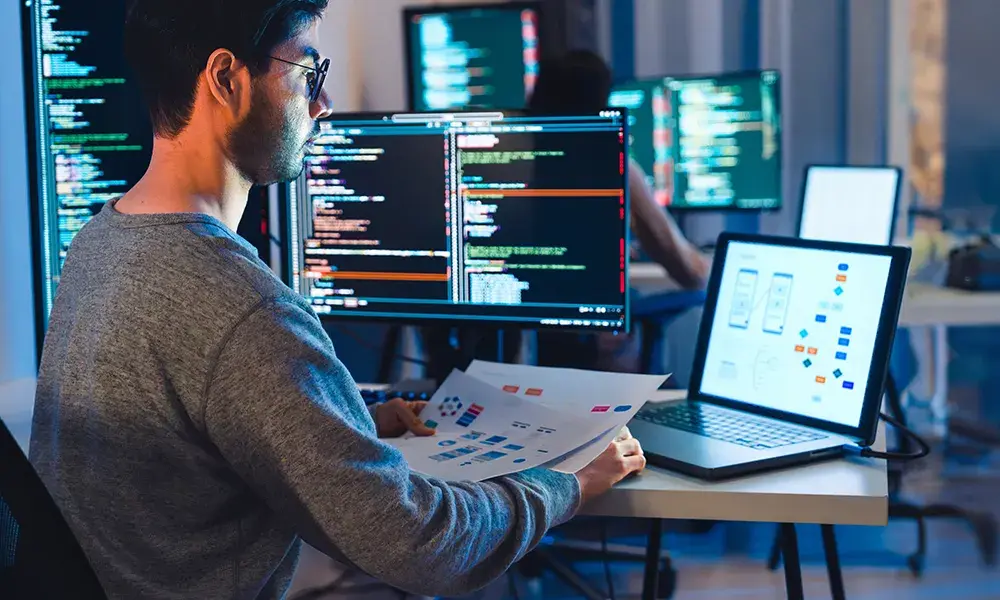

Data Harbor Platform SDKs
SDKs for Go, JavaScript/TypeScript, and Java, plus gRPC and a CLI. The APIs we publish are the APIs we build with.

Your First TDF in About 10 Minutes
Run the OpenTDF quickstart for basic encrypt and decrypt. The full ABAC scenario takes about 30 minutes, with no account needed.
AI Agents
Give each agent its own identity and entitlements. Every request it makes is checked against your policy, just like a person's.

TDF, an Open Standard
TDF originated at the NSA and is open on GitHub. Read the spec, and verify exactly how it works.
The Data Harbor Platform
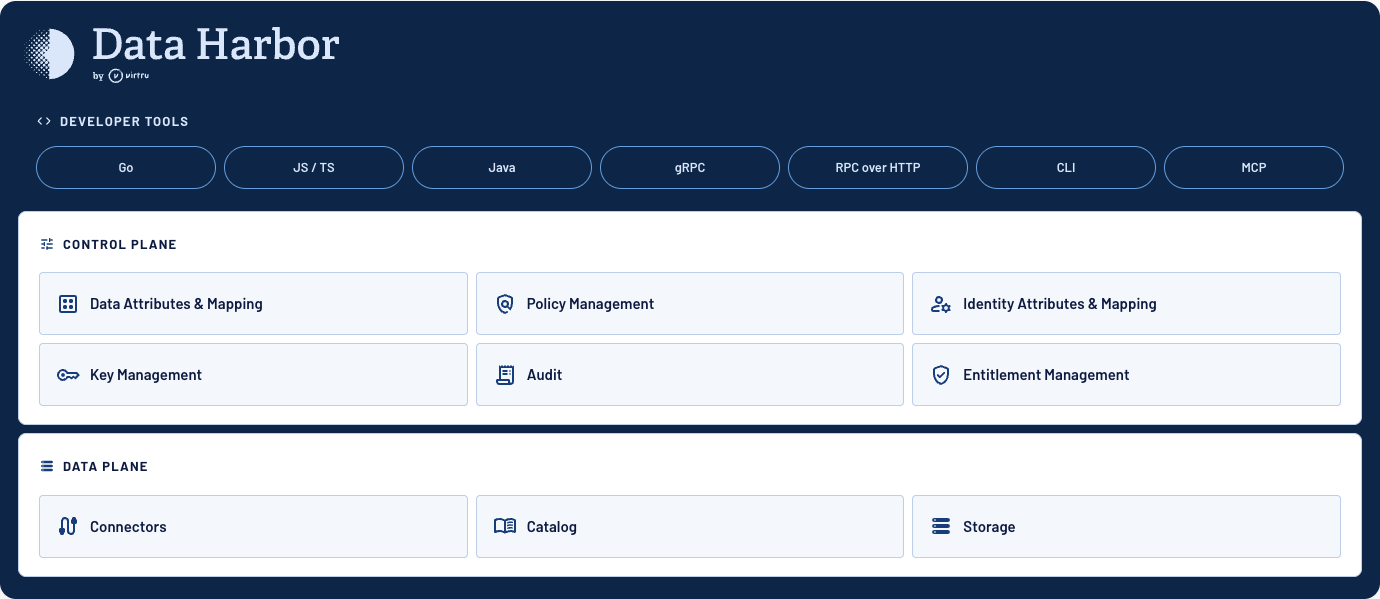
Requests come from people, partner systems, and AI agents. You write the rules; the platform makes the call and enforces it. Its control plane holds policy, attributes, entitlements, key access, and audit, and connects to the identity providers, tagging tools, and policy systems you already run.
The platform is pre-wired to the systems on which your Attribute-Based Access Control (ABAC) decisions depend. DSPM, DLP, and classification platforms feed data attributes into the Tagging Service. IdPs and ICAM systems supply subject entitlements for both human and AI identities. HSMs, cloud KMS, and S3-compatible storage plug in at the infrastructure layer.
Your posture management, DLP, and classification tools feed data attributes in through the Tagging Service. Your identity providers supply entitlements for people and AI agents. Hardware security modules and cloud key management plug in underneath.
Start Free. Scale Up.
Build for production on the Virtru Data Harbor Platform, and prototype for free on the open-source OpenTDF SDKs.
Build for Scale on the Data Harbor Platform.
Built for production, with enterprise extensions on top of everything in OpenTDF. Deploy it self-managed, in your cloud, on-premises, or fully air-gapped.
- Platform SDKs or Go, JavaScript/TypeScript, and Java, plus a CLI, and MCP for AI-assisted administration
- Data tagging, and ZTDF (ACP-240) and IC-TDF formats
- Policy import and export, and certificate management · Encrypted search, plus storage, SQL, and vector connectors

Read the SDK Docs
View the Developer Documentation
To try the Data Harbor Platform, request evaluation access, and we'll set you up with the SDKs, training, and an environment to build in.
Prototype for Free on OpenTDF
TDF originated at the NSA and is now an open standard. OpenTDF is its open-source implementation, with Virtru as lead contributor. No account needed: run the code, read the spec, and check exactly how it works before you build on it.
- ABAC policy, authorization, and the Key Access Service
- SDKs for Go, Java, and JavaScript
- BSD-3-Clause-Clear license
- Open standards, no proprietary lock-in
Start Building
The QuickStart covers basic encrypt and decrypt in about 10 minutes, or the full ABAC scenario in about 30. You'll need macOS, Linux, or Windows (WSL2), a container runtime (Colima or Docker), 4 GB of RAM, 10 GB of free disk, and admin access. Stuck? Ask in OpenTDF GitHub Discussions
Connect Your Data Stores
Connectors sit between your applications and your data, so policy applies from the moment data is stored or queried, with little or no change to your application code.
Storage Connector
Protect objects in any S3-compatible store, including AWS, Google Cloud Storage, MinIO, and Cloudflare. Every read is checked against your policy.
- Works with S3-compatible stores
- Objects stay protected
- Every read is checked

SQL Connector
Query protected SQL tables through a Trino-compatible connector. Rows and columns are released only to the entitled people or agents .
- Row and column control
- Standard SQL queries
- Every query is recorded

Vector Connector
Govern the vector stores behind your AI. Retrieval over TDF-protected chunks in pgvector returns only what the person or agent is entitled to see.
- Policy-aware retrieval
- Built for AI agents
- Works with LangChain
How Others Are Building
See how others, from gateway developers to messaging and identity providers, have built on the Data Harbor Platform. Choose one to see how it plugs in.

AI gateway
Kong governs which tools an agent can call. The Data Harbor Platform protects the object based on entitlements and enforces it through its enforcement point in Kong's gateway.
Kong AI Gateway
MCP tool calls
One identity, two layers
Read the Case Study

Chat
The Data Harbor Platform makes the call on every file at upload and again at view, and enforces it through its enforcement point in Mattermost: the Zero Trust Data Format (ZTDF) Bridge plugin.
Mattermost
ZTDF Bridge plugin
Check at upload & view
Read the Case Study


Systems Integrator
Booz Allen builds the Data Harbor Platform into mission architectures and delivers it inside the customer's accreditation boundary.
Booz Allen Hamilton
Mission-system integration
Accreditation-boundary delivery
Read the Case Study


Video
The Data Harbor Platform confirms entitlements when a meeting is scheduled and again when someone joins, and enforces it through its enforcement point in Pexip, so clearance changes after the invite still count.
Pexip
Join validation
Classification-aware scheduling
Read the Case Study
Identity
Dapple captures a signed human approval for each agent request. The Data Harbor Platform compares that approval with the agent's entitlements and the data's attributes, under your policy, on every request.
Dapple Security
Revocable anytime
Signed human grant
Read the Case Study
Chat
The Data Harbor Platform checks each channel membership against current entitlements and enforces it in Rocket.Chat, so revoked access ends the membership.
Rocket.Chat
Entitlements sync
Add-time validation
Read the Case Study
File Security
Glasswall's TDF Bridge rebuilds encrypted files clean at the domain boundary. The Data Harbor Platform makes the call and enforces it at the key: the bridge gets a key only when your policy allows.
Glasswall
TDF bridge
Signed provenance
Read the Case Study
AI gateway
Kong governs which tools an agent can call. The Data Harbor Platform protects the object based on entitlements and enforces it through its enforcement point in Kong's gateway.
Kong AI Gateway
MCP tool calls
One identity, two layers
Read the Case Study
Chat
The Data Harbor Platform makes the call on every file at upload and again at view, and enforces it through its enforcement point in Mattermost: the Zero Trust Data Format (ZTDF) Bridge plugin.
Mattermost
ZTDF Bridge plugin
Check at upload & view
Read the Case Study
Systems Integrator
Booz Allen builds the Data Harbor Platform into mission architectures and delivers it inside the customer's accreditation boundary.
Booz Allen Hamilton
Mission-system integration
Accreditation-boundary delivery
Read the Case Study
Video
The Data Harbor Platform confirms entitlements when a meeting is scheduled and again when someone joins, and enforces it through its enforcement point in Pexip, so clearance changes after the invite still count.
Pexip
Join validation
Classification-aware scheduling
Read the Case Study
Identity
Dapple captures a signed human approval for each agent request. The Data Harbor Platform compares that approval with the agent's entitlements and the data's attributes, under your policy, on every request.
Dapple Security
Revocable anytime
Signed human grant
Read the Case Study
Chat
The Data Harbor Platform checks each channel membership against current entitlements and enforces it in Rocket.Chat, so revoked access ends the membership.
Rocket.Chat
Entitlements sync
Add-time validation
Read the Case Study
File Security
Glasswall's TDF Bridge rebuilds encrypted files clean at the domain boundary. The Data Harbor Platform makes the call and enforces it at the key: the bridge gets a key only when your policy allows.
Glasswall
TDF bridge
Signed provenance
Read the Case Study
Build an Integration
The Data Harbor Platform is fully extensible. Build an enforcement point into your product: it asks the platform for a decision, and your product carries it out.
Build for government, defense, and enterprise customers. Whether you're a systems integrator on one customer's program or an ISV shipping TDF protection in your product, you build the enforcement point. The platform makes the call and handles the cryptography.

Integration Points
- SDKs: Go, Java, and JavaScript libraries for creating and reading TDF objects
- Policy Service API: Programmatic access to attribute definitions and policy decisions
- Key Access Service: OIDC-authenticated key release tied to ABAC entitlements
Providing upstream data discovery and tagging. Posture management, DLP, and classification tools. Feed labels into enforcement through the Tagging Service API and bidirectional sync.
Integration Points
- Tagging Service API: Feed classification metadata into the platform for automatic policy mapping
- Attribute definitions: Map your classification taxonomy to platform attribute definitions
- Bidirectional sync: Query the platform for protection status to enrich your discovery data
Providing entitlement attributes for access decisions. ABAC access decisions depend on knowing who is requesting access and what entitlements they hold. Your identity platform provides the subject attributes through OIDC and OAuth 2.0 — roles, clearances, organizational affiliations, and more. The platform evaluates entitlements and compares against data policies. Support extends to both humans and AI agents, including service accounts.
Integration Points
- OIDC / OAuth 2.0: Standard token-based integration with any compliant provider
- Attribute mapping: Map identity claims to Platform entitlements
- Entity resolution: Human, service account, and AI agent identities
Resources
Extending the Platform across the infrastructure stack. Infrastructure partners provide the foundational layers on which the Virtru Data Harbor Platform leverages — hardware security modules, storage, cross-domain solutions, and more. Integrations range in scope from protocol compatibility to co-engineering, depending on what the partner's platform requires and the customer's needs.

Where We Partner
- Hardware security modules (HSMs) — Vendor-specific deep integrations come through joint engineering, so the platform takes full advantage of the HSM's native capabilities. PKCS#11 is the baseline interface for broad compatibility.
- Storage — Storage platforms integrate with the platform's ingestion and enforcement layer. Protocol coverage expands as the roadmap and partnerships evolve.
- Cross-domain solutions (CDS) — Joint engineering enables policy-governed data movement across classification boundaries. CDS integrations are in production today, with additional partnerships under development.
For the current list of production infrastructure integrations, see the Partner Directory or Architecture Guide.
If you're a cloud or infrastructure provider: If you’re not listed in our directory, let’s start the conversation.
Developer Resources
-
Developer Docs: getting-started guides, API reference, and integration patterns. Free.
-
Architecture Overview: Platform components, data flows, and deployment models
-
API Reference: gRPC and HTTP APIs for policy, attributes, key access, and tagging
-
OpenTDF Quickstart: your first TDF in about 10 minutes
-
TDF Specification: the open standard, on opentdf.io
-
GitHub Discussions: Ask questions, share solutions, report issues
-
Partner Support: Dedicated technical support for technology partners
Sign up for a customer or partner bootcamp, and get hands-on time with the Data Harbor Platform's SDKs, policy model, and deployment. View Training Information
Ready to Build on the Data Harbor Platform?
Tell us what you plan to build, and we'll equip you with the SDKs, training, and support to make it a reality.
6,100 CUSTOMERS TRUST VIRTRU FOR DATA SECURITY AND PRIVACY PROTECTION.